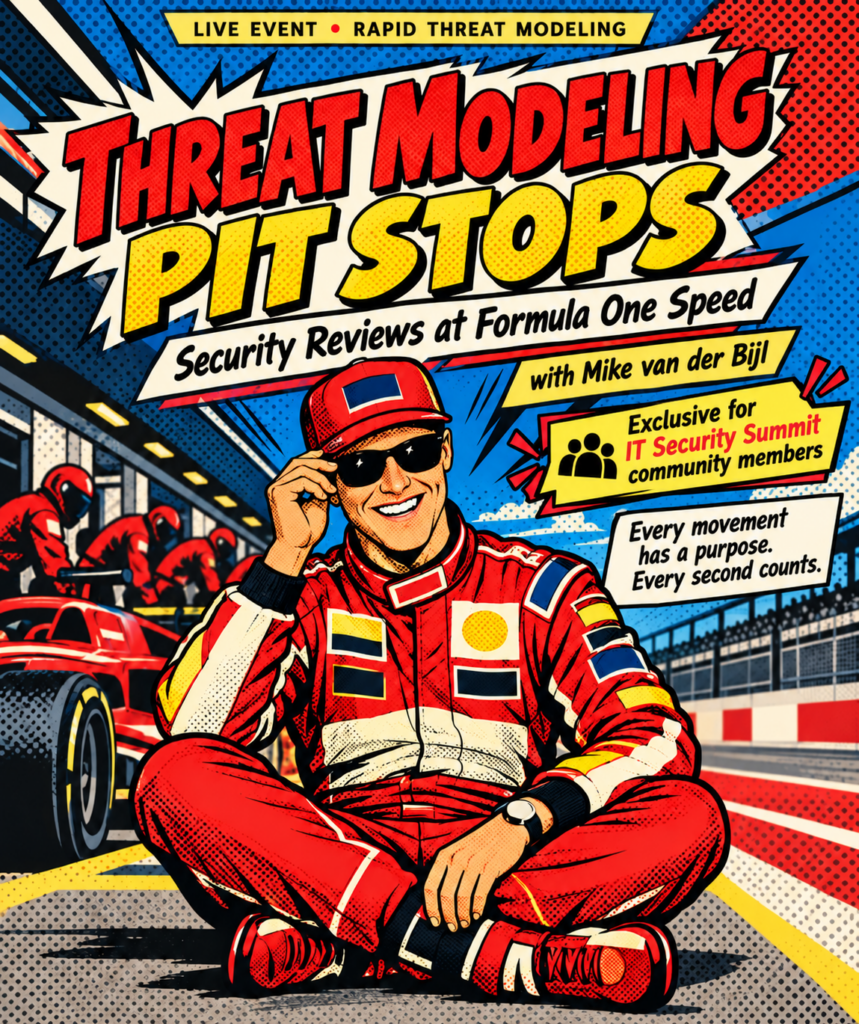
Threat Modeling Pit Stops
Security Reviews at Formula 1 Speed
Live on November 09, 2026 | 12:00 - 13:00
Tage
Stunden
Minuten
Sekunden
🇬🇧 English

Sign Up for Free
Privacy Notice
Your privacy is important to us! We will only use your personal data to manage your user account and your use of S&S Media products. If you do not agree to these terms, we unfortunately cannot provide you with access to the content. You can unsubscribe from notifications at any time. For more information, please refer to our Privacy Policy. By clicking „Send“, you agree to the terms outlined above regarding the use of your personal data to access the specified content.From Security Risks to Action
If only your security review had a pit crew Threat modeling takes time. But long reviews leave engineering teams waiting for a practical answer: which attack scenarios pose the greatest risk, and what should they tackle first?
The longer it takes to reach that decision, the longer it takes to turn the findings into work.
Changing four tires can take an hour at a garage. However, a Formula 1 pit crew gets the job done in seconds. That comparison captures the idea behind Rapid Threat Modeling: a focused process can change how quickly the work gets done.
Join Mike van der Bijl, you’ll learn how to:
- Inspect an application quickly, focusing on the components most likely to fail.
- Identify the highest-risk attack scenarios in minutes rather than days.
- Prioritize risks so teams know where to focus their security effort.
- Turn findings into actionable engineering work, connecting the review directly to what happens next.
Security Reviews at Formula 1 Speed
Security reviews do not have to take days to deliver valuable results. Rapid Threat Modeling provides a focused approach to quickly inspecting an application, identifying the highest-risk attack scenarios, and prioritizing the components most likely to fail. Instead of analyzing every part of a system with the same level of effort, teams can concentrate on the risks that matter most and turn their findings directly into actionable engineering work.
A Formula 1 team can replace four tires, inspect the car, and send a driver back onto the track in under three seconds. The difference is not the work itself, but the process. In this session, Mike van der Bijl uses the Formula 1 pit stop as a metaphor for security reviews, showing how teams can apply Rapid Threat Modeling to assess applications in minutes rather than days, focus on critical risks, prioritize attack scenarios, and translate security findings into concrete actions.
Focus on the Risks That Matter Most
The goal is not simply to identify more security issues, but to focus quickly on the risks that can have the greatest impact. Rapid Threat Modeling combines speed with a structured process, helping teams quickly assess an application, identify critical components, and prioritize the attack scenarios that deserve the most attention. This focused approach makes it easier to turn security findings into concrete engineering actions, while keeping reviews practical and efficient. Instead of becoming a lengthy standalone activity, threat modeling can become a repeatable part of the development process that helps teams spot risks early and act on them quickly.
Expert Knowledge for
Security engineers who want to make threat modeling faster and more focused.
Software developers who want to identify and prioritize security risks early.
Software architects who need to assess critical attack scenarios in their applications.
DevSecOps teams looking to integrate focused security reviews into development.

Join us and learn how to...
apply Rapid Threat Modeling to perform focused security reviews.
identify the highest-risk attack scenarios in minutes rather than days.
focus security analysis on the components most likely to fail.
prioritize risks and turn findings into actionable engineering work.
- combine speed and focus to make security reviews more practical.

Mike van der Bijl - DHL eCommerce BeNeLux
Mike van der Bijl works in cybersecurity, threat modeling, and IT management, with a focus on practical security approaches and interdisciplinary collaboration. In this session, he introduces Rapid Threat Modeling and shows how teams can use a focused process to identify critical risks, prioritize attack scenarios, and translate security findings into concrete engineering actions.